The 3Cs: A Framework for AI Agent Security
Every useful agent has access to private data, exposure to untrusted content, and the ability to act externally. You cannot train or prompt that away. The 3Cs are the three places you can actually draw a boundary.
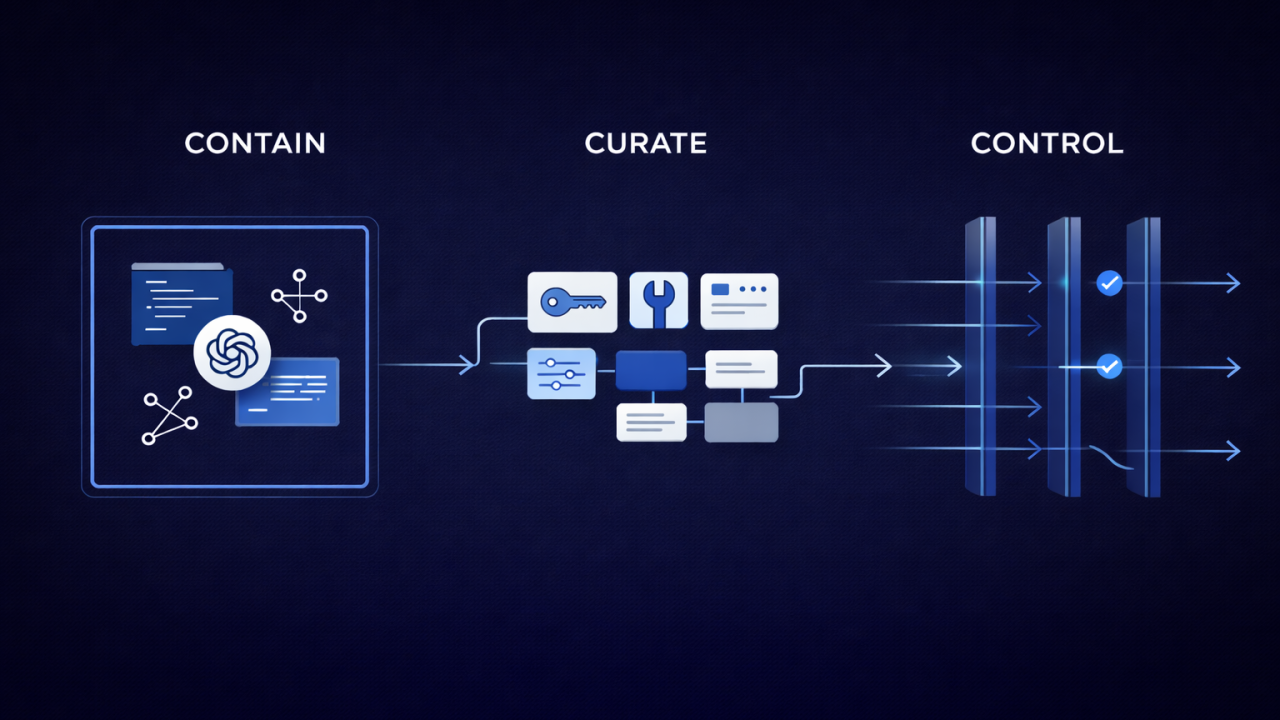
The Three Cs
Where the agent runs
Isolate each agent session so a fault or a compromise cannot reach the host, the network, or the filesystem beyond what you allow.
Without it: an agent on the laptop has the developer’s full reach.
What the agent can see
Define the tools, context, and credentials available to each agent session. A deliberate environment makes execution predictable. An unstructured one is just autonomy without guardrails.
Without it: agents act across your entire system with no defined scope.
What the agent can call
Govern which MCP servers and tools are available, with everything logged and unvetted servers denied by default.
Without it: no record of what an agent touched or on whose behalf.
How Docker Enforces the 3Cs
Containment
Every agent session runs in a microVM-isolated sandbox. A hardware boundary, not a container or OS-level sandbox the agent can route around
Curation
Each session gets a curated environment: exactly the tools, context, and credentials it needs for the task. Nothing more.
Control
The MCP Gateway routes every tool call through one chokepoint, authenticated, authorized, and logged. Policy set once, enforced on every machine.
See the 3Cs enforced on a real machine.
Thanks for reaching out.
One of our AI governance specialists will contact you soon to walk your team through how it works and discuss your requirements.